One page for the whole homelab
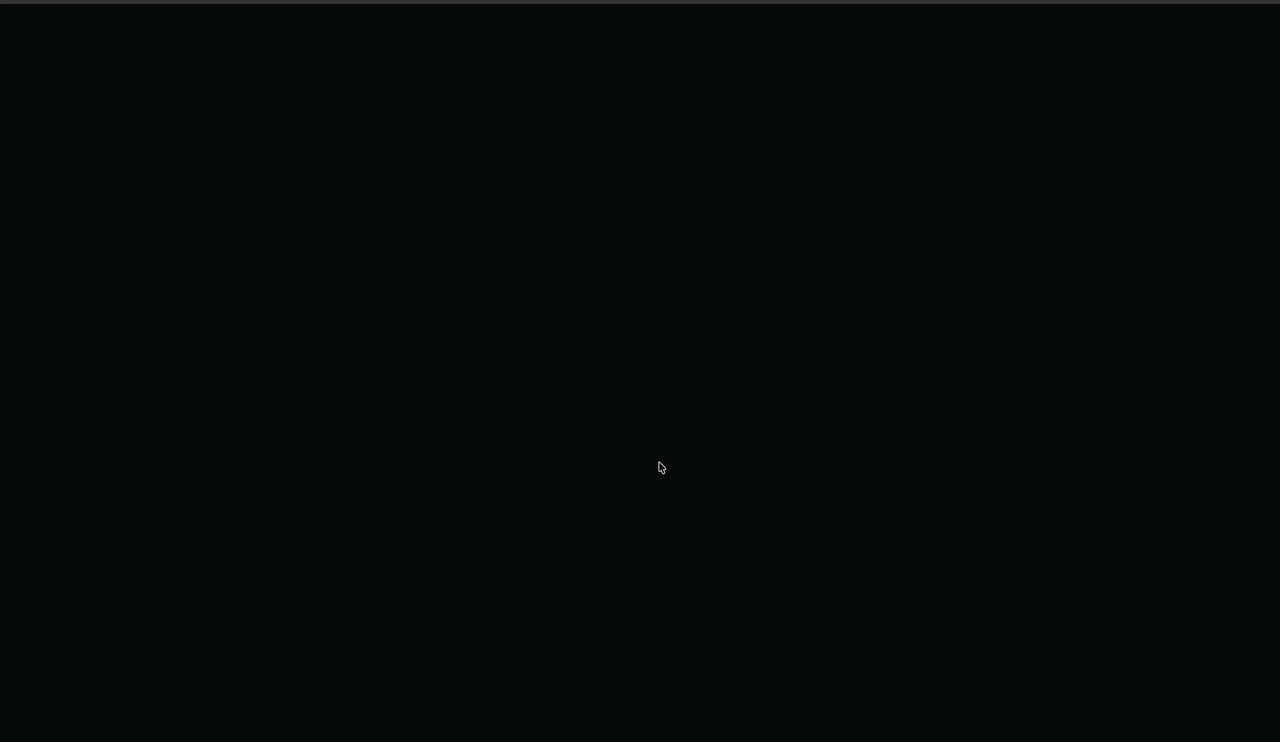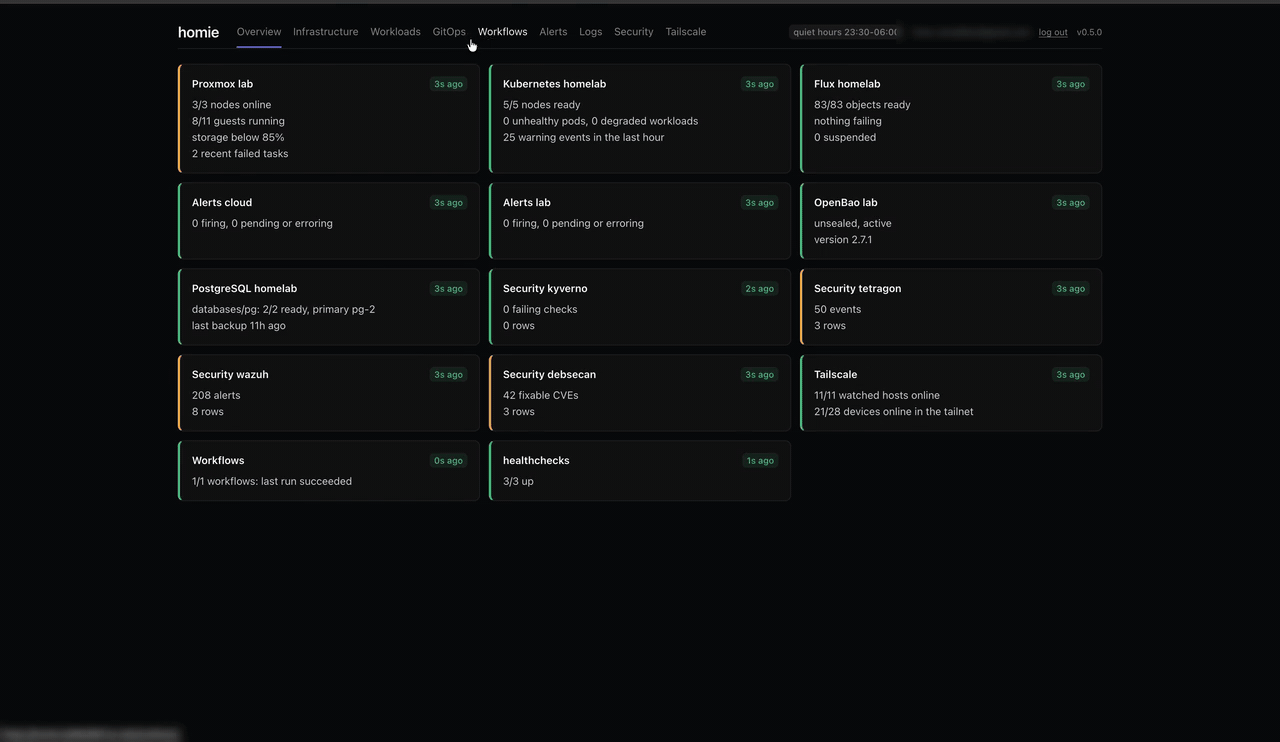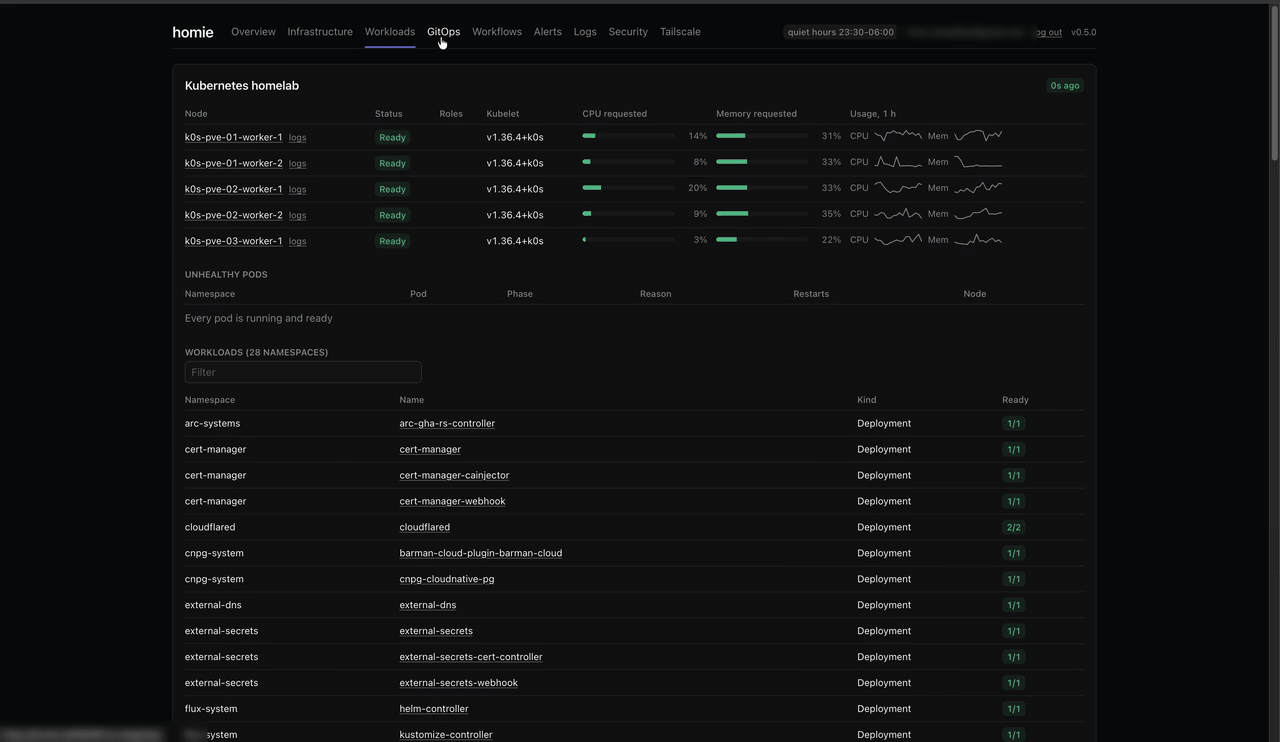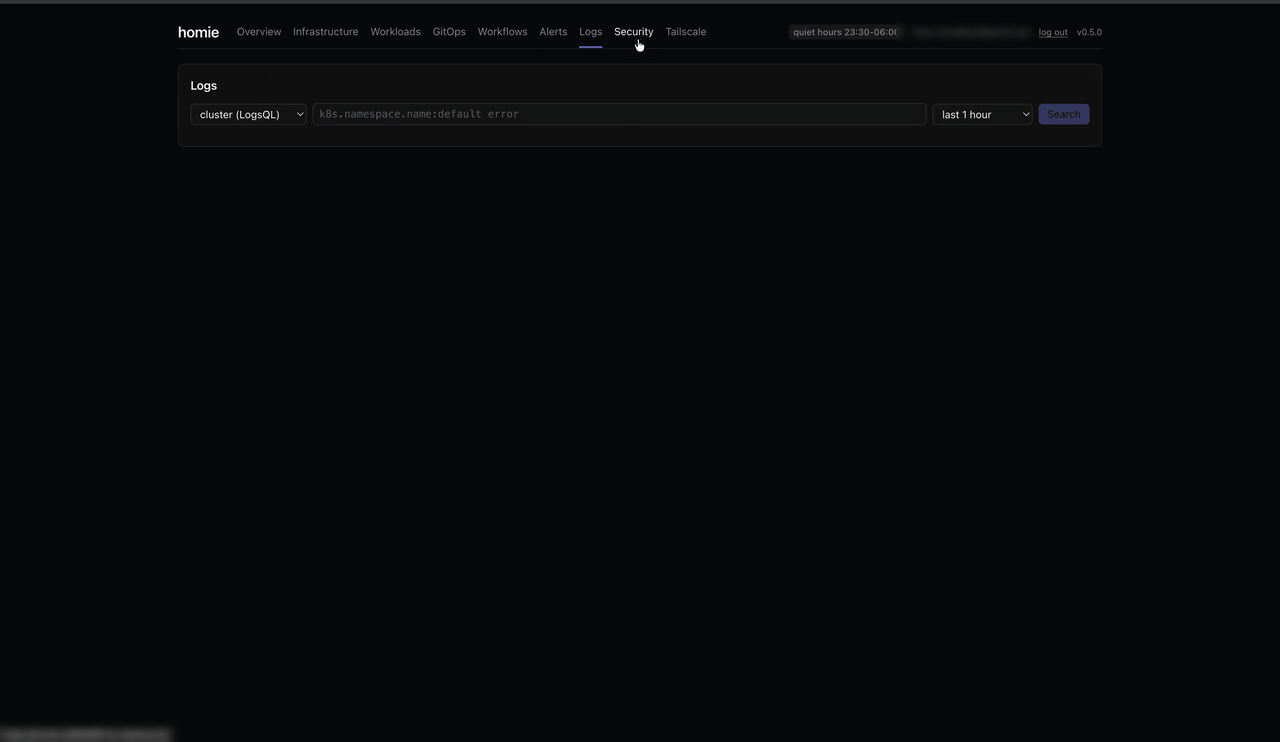
Hypervisor hosts and guests, Kubernetes workloads, GitOps state, alerts, logs and security findings, on one calm page. A few safe actions, and deep links to the specialist UIs for everything else.
The demo is the author's real lab, read-only. The lab sleeps from 23:30 to 06:00 WIB (UTC+7).
What it shows
Every integration is optional. Configure only what your lab has; the pages for the rest never appear.
Proxmox VE
Nodes, guests, storage, HA and failed tasks for one or more clusters, with CPU and memory sparklines. Start, shut down and reboot guests; protected tags ask you to type the name first.
Any conformant cluster
Nodes, workloads, unhealthy pods and warning events from k0s, k3s, RKE2, Talos, kind or a managed cloud. Auth by kubeconfig, in-cluster ServiceAccount, or the user's own OIDC token.
Flux and Argo CD
Sources, Kustomizations and HelmReleases with one-click reconcile; Argo CD Applications with refresh. Helm releases show chart, version and status, never values.
Alerts and logs
Firing and pending alerts from any number of Grafana instances, self-hosted or Grafana Cloud. Search VictoriaLogs or Loki, prefilled from a pod or a node.
Findings in one place
Kyverno policy reports, Tetragon runtime events, Wazuh alerts and debsecan CVE counts, read through Grafana. Plus OpenBao seal state and CloudNativePG backup age.
Pipelines and the outside view
Terraform plan and apply runs (any GitHub Actions workflow) through a read-only GitHub App, picked in the UI. Tailscale and healthchecks.io tell you what is down when the lab itself is.
How it works
A single Rust binary with the web UI embedded. No database, no agents, no sidecars.
- Runs where you want. In the cluster behind any OIDC provider (Authentik, Keycloak, Authelia, Pocket ID, Zitadel, Cloudflare Access, Google), or on a laptop bound to loopback, so the lab's last known state stays visible when the cluster is down.
- Live. Results stream to the browser over server-sent events; Kubernetes and Flux changes appear within seconds. One shared cache serves every tab.
- Quiet hours. Parts of the lab that are powered off on a schedule show as "scheduled off", not as an outage.
- Read-only by default. Actions are few, confirmed, and logged with the user who ran them.
- Configured, not clicked. One TOML file and
HOMIE__*environment variables. Secrets come from env, files or a command (Keychain,pass,op read).
A minimal config
Point it at what you have. homie check tests every integration before you start.
# ~/.config/homie/config.toml
[proxmox.lab]
endpoints = ["https://pve1.example:8006"]
token = { env = "PVE_TOKEN" }   # PVEAuditor, + VM.PowerMgmt for power

[kubernetes.home]
auth = "kubeconfig"

[grafana.home]
url = "https://grafana.example"
token = { cmd = "security find-generic-password -s grafana -w" }

[quiet_hours]
window = "23:30-06:00"
timezone = "Europe/Berlin"
Install
Pick one. Releases ship macOS and Linux binaries, a multi-arch image, a Helm chart and a Homebrew formula.
brew install franzramadhan/tap/homie
homie check      # validates the config and tests every integration
homie serve      # http://127.0.0.1:7777
mise use -g github:franzramadhan/homie
homie check
homie serve
helm install homie oci://ghcr.io/franzramadhan/charts/homie \
  -n homie --create-namespace -f my-values.yaml
# config goes in the `config` value, secrets in `existingSecret`
docker run --rm -p 127.0.0.1:7777:7777 \
  -e HOMIE__LISTEN=0.0.0.0:7777 -e HOMIE__ALLOW_UNAUTHENTICATED=true \
  -v ./config.toml:/etc/homie/config.toml:ro -e HOMIE_CONFIG=/etc/homie/config.toml \
  ghcr.io/franzramadhan/homie:latest serve
From zero to a dashboard
The usual path for a new lab.
Create read-only credentials
A Proxmox token with PVEAuditor, a Grafana Viewer token, a kubeconfig or ServiceAccount with view rights.
Write the config
Start from examples/local.toml or server-oidc.toml; reference secrets, never paste them.
Run homie check
Every integration answers ok, or tells you exactly what failed and why.
Serve it
On your laptop, or in the cluster behind your OIDC provider. Add actions when you trust it.
Safe to point at your lab
A dashboard holds keys to everything it shows. Homie treats that seriously.
- Server-side sessions, an opaque cookie, CSRF and Origin checks on every write, and a Host check against DNS rebinding.
- Your identity reaches Kubernetes. With
forward_token, the apiserver sees the logged-in user, so its RBAC and audit log apply. - Roles. A read-only view limited to some pages, explicit namespaces and tagged guests, enforced by Kubernetes RBAC through an impersonated ServiceAccount, with addresses redacted.
- TLS per integration: a custom CA, a different server name, or opt-in skip-verify that is flagged in the UI and the logs.
Built in the open
Every feature starts as an RFC, is discussed, then built and tested against a real homelab before release.
- Tested. Over 130 tests against fake Proxmox, Kubernetes, Grafana, GitHub and OIDC servers; line coverage around 98%.
- End to end. Each change runs in the author's k0s cluster before it ships.
- Design docs. rfc/ and the roadmap explain what exists and why.
- MIT licensed. Alpha (0.x): config keys may still change between versions.